Talvium · World Secure ComputeView assurance status

Talvium for government & sovereign missions

Trusted AI and compute for sovereign missions.

Build, deploy, and govern mission workloads across secure compute environments designed around jurisdiction, identity, data, energy, and evidence.

Program in development. Availability and certifications are not implied.

Secure analysts coordinating a sovereign compute mission
World Secure ComputePolicy-aware operations across bounded environmentsSee the federation model

Overview

Built for the mission, secured by design.

Talvium connects compute, AI, data, energy, and operating evidence without treating every geography or workload as the same.

Compliance and security built in

Architect controls against named frameworks, publish the exact scope, and separate a target from an awarded authorization.

AI for your mission

Place models, knowledge, agents, and inference inside the same region, identity, and evidence boundary as the workload.

Sovereign control for your data

Define where data is stored and processed, who can operate the service, who controls keys, and which laws apply.

Build, migrate, and federate

Move portable workloads only to eligible nodes; refuse placement or recovery when policy cannot be satisfied.

Energy-aware infrastructure

Make power, thermal conditions, storage resilience, connectivity, and maintenance visible to capacity decisions.

Discover Talvium security
Scientists reviewing governed AI results
Original Talvium concept visualization

Compute environments

Secure compute for every mission boundary.

Choose the environment first. Catalog, connectivity, operators, geography, and assurance are then scoped to that boundary.

World Secure Compute

One federated platform. Five deliberate security boundaries.

Talvium is designing a common policy, identity, evidence, and capacity layer across global, sovereign, enclave, national, and disconnected environments. Availability and authorization remain specific to each deployed service boundary.

FedRAMP HighTarget
StateRAMP HighTarget
DoD SRG IL2 / IL4 / IL5Target
DoD SRG IL6Sponsor-gated
ICD 503 / ICD 705Sponsor-gated
JSIG PL3Sponsor-gated
FIPS 140-3Validated modules required
ISO/IEC 27001Target
Explore this environment

Talvium assurance program

Full certification, authorization, and framework names.

All entries below are targets, mappings, scoped requirements, or sponsor-gated pathways unless an exact record is explicitly marked achieved.

U.S. government authorization

FedRAMP High — JAB P-ATOTarget
StateRAMP HighTarget
DoD Cloud SRG IL2 — PATarget
DoD Cloud SRG IL4 — PATarget
DoD Cloud SRG IL5 — PATarget
DoD Cloud SRG IL6 — PASponsor-gated
ICD 503 — ATOSponsor-gated
ICD 705 facility accreditationSponsor-gated
JSIG Protection Level 3 — ATOSponsor-gated

Government and regulated data

CJIS Security PolicyMapping target
IRS Publication 1075Mapping target
DFARS 252.204-7012Contract target
NIST SP 800-171Mapping target
CMMCAssessment target
ITARScope target
EARScope target
HIPAAControl target
Agency Authorization to Operate (ATO)Agency-specific

Security, privacy, and resilience

FIPS 140-3 CMVPValidated modules required
FIPS 140-2 CMVPLegacy transition only
ISO/IEC 27001Certification target
ISO/IEC 27017Mapping target
ISO/IEC 27018Mapping target
ISO/IEC 27701Certification target
ISO/IEC 20000-1Certification target
ISO 22301Certification target
SOC 2 Type IIReport target

Cloud, payments, privacy, and AI

CSA Cloud Controls Matrix (CCM)Mapping target
CSA Security, Trust, Assurance and Risk (STAR)Registry target
PCI DSSScoped target
GDPRLegal and control mapping
National privacy lawRegion-specific mapping
ISO/IEC 42001Certification target
NIST AI Risk Management FrameworkOperating-framework target

Status matters: a named framework is a program objective until Talvium publishes an authoritative record for the exact entity, service, region, facility, configuration, and date.

View the complete assurance catalog

Mission use cases

Advance your mission.

Start with the operating decision, then compose the eligible Talvium environment, controls, capacity, AI, and evidence.

Mission solutions

Public services with data control built into the deployment

Support casework, language access, geospatial analysis, knowledge assistance, and public-program analytics while keeping residency and operator responsibilities visible.

Explore the mission pathway
Sovereign AIRun approved models within a declared regional and key-control boundary.Controlled data exchangeShare only the permitted data or derived result across institutions.Evidence-led operationsKeep configuration, access, and change records ready for review.Concept visualization

Infrastructure program

From candidate land to mission-ready capacity.

Talvium is building a proof chain across land authority, site suitability, utilities, energy, network, facilities, compute, operations, and assurance.

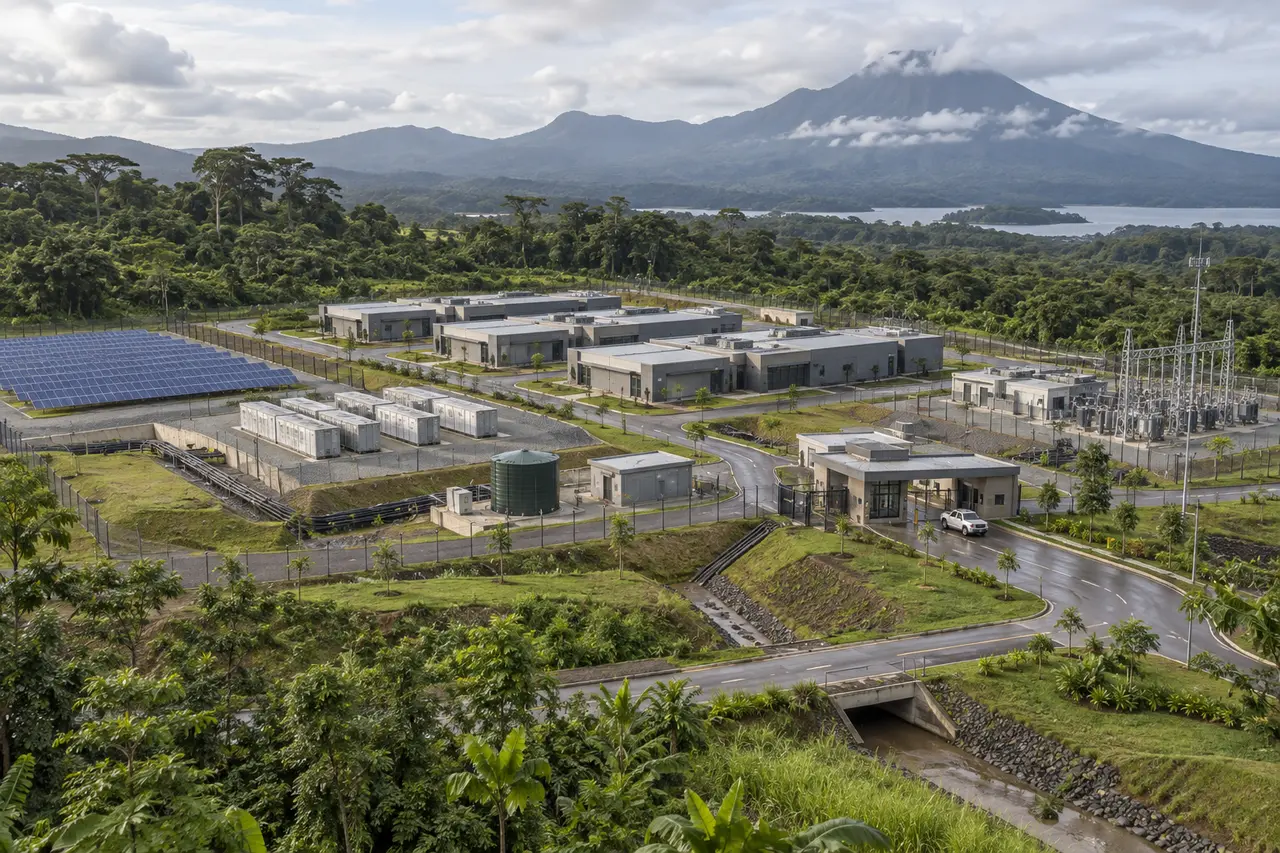
Conceptual secure compute campus in a tropical landscape
Concept visualization — not a completed facility

Africa Site 01 · Southwest Cameroon

A candidate anchor for federated compute.

Management reports a land position of approximately 4,000 acres. Talvium is treating that statement as a diligence input—not as proof of title, surveyed acreage, buildable area, power, fiber, permitting, mineral rights, or available compute.

  • Title, authority, survey, boundary, and encumbrance verification
  • Geotechnical, volcanic, flood, environmental, and community diligence
  • Power, water, fiber, roads, security, and logistics validation
  • Modular compute, clean-energy, and battery-resilience phasing
01Candidate site diligenceManagement-reported land position · independent validation required
02Two-node federation proofSynthetic, unclassified demonstrator · in development
03Assurance programFramework mapping and evidence architecture · targets published

Program updates

What’s new for Talvium.

Products and services

Build with the Talvium platform.

Every public capability is lifecycle-labeled and becomes purchasable only for a published region, environment, configuration, capacity, support model, and contract.

AI · Planned

Talvium AI Studio

Models, agents, knowledge, evaluation, and deployment within declared region and policy boundaries.

Explore

AI · Planned

Secure AI Services

Document, language, speech, vision, and multimodal services with provider and region provenance.

Explore

Compute · Planned

Accelerated Compute

GPU, HPC, batch, and inference capacity represented by eligible configuration and power envelope.

Explore

Regions · Planning

Sovereign Regions

Jurisdiction-aware environments with region-specific residency, operations, keys, and evidence.

Explore

Federation · In development

Federation Control Plane

Identity, capacity registry, policy placement, observability, metering, and authorized failover.

Explore

Security · Reference design

Secure Enclaves

Isolated landing zones and compute cells for sponsor- or customer-defined sensitive workloads.

Explore

Security · Design target

Confidential Compute

Hardware-backed attestation and data-in-use protections for approved configurations.

Explore

Edge · Reference design

Talvium Local & Edge

Connected, intermittent, and disconnected operation with signed updates and controlled sync.

Explore

Data · Planned

Data Fabric

Governed databases, object storage, lakehouse, catalogs, exchange, and analytics by region.

Explore

Beyond compute

Energy and materials assurance for resilient infrastructure.

Talvium connects workload commitments to measured power, thermal limits, battery condition, network state, and maintenance readiness. Local minerals remain a separate diligence track until rights, geology, economics, permitting, provenance, and qualification are verified.

Explore the infrastructure layer

Resources

Explore Talvium guidance.

Planning guide

01

Select a Talvium operating environment

Compare service breadth, isolation, operator control, connectivity, and assurance.

Read the guide

Assurance

02

Review every certification program and status

See the target, mapping, assessment, authoritative record, and exact service boundary.

Read the guide

Architecture

03

Build a sovereign AI landing zone

Start with identity, data location, model provenance, keys, policy, and evidence.

Read the guide

Site program

04

Examine Africa Site 01 diligence

Separate management-reported land access from title, survey, power, fiber, hazard, and permitting evidence.

Read the guide

FAQ

Frequently asked questions.

01What is Talvium?

Talvium is developing certification-led secure federated compute for government, sovereign, scientific, critical-infrastructure, and industrial missions.

02Is Talvium currently a production cloud?

No production region or generally available capacity is represented as live in this V2 preview.

03Is Talvium affiliated with Microsoft Azure?

No Microsoft or Azure affiliation, technology relationship, authorization inheritance, service parity, or scale is claimed. Azure Government informed this site's information architecture only.

04What does World Secure Compute mean?

It is Talvium's model for policy-governed capacity across multiple jurisdictions and operating environments without erasing local control boundaries.

05Which environments are planned?

Global Compute, Sovereign Region, Secure Enclave, Private / National Cloud, and Disconnected Edge.

06Does Talvium hold the certifications shown here?

Not unless an item is explicitly labeled Achieved and linked to an authoritative, scope-specific record. Current items are targets, mappings, assessment plans, or sponsor-gated pathways.

07What is the status of the approximately 4,000-acre site?

It is a management-reported candidate land position in Southwest Cameroon. Title, survey, usable acreage, encumbrances, power, fiber, environmental approvals, and construction readiness require independent diligence.

08How are energy and materials connected to compute?

Power availability, thermal conditions, battery resilience, and maintenance affect deployable capacity. Mineral potential is separate optionality and is not treated as verified supply or value.

09How does the first federation proof work?

The first planned milestone is a two-node, synthetic, unclassified demonstrator showing policy placement, denial, bounded recovery, and evidence export.

10How can an organization begin?

Create a nonsensitive capacity brief describing mission, jurisdiction, workload, environment, connectivity, continuity, timing, and evidence priorities.
Start with Talvium

Turn a mission requirement into a bounded plan.

Secure mission planning team

Mission owners

Request a capacity assessment.

Define a nonsensitive workload, jurisdiction, environment, timing, continuity, and evidence envelope.

Build your capacity brief
Conceptual Talvium compute campusConcept visualization

Governments and partners

Propose a region or enabling layer.

Bring local authority, infrastructure, technology, energy, financing, or mission demand into a structured validation path.

Partner with Talvium

Talvium is in development. Services, capacity, regions, facilities, customers, partnerships, classified operations, and certifications are not represented as available or achieved unless an exact public record says so.

World Secure Compute/Accessibility/accessibilityCapacity brief builder/capacity-briefBegin with a nonsensitive, bounded requirement/contactInfrastructure evidence beneath the compute promise/energy-materialsStorage is a tested service component, not a sustainability prop/energy-materials/battery-resilienceDesign repair and end-of-life before deployment/energy-materials/circularityStart with contracted, measurable power/energy-materials/clean-powerMake power and thermal state part of workload eligibility/energy-materials/energy-aware-schedulingTreat mineral potential as an option until proven/energy-materials/materialsDesign the power system for the service promise/energy-materials/powerNo region without a site evidence index/energy-materials/site-evidenceFollow infrastructure inputs through their evidence chain/energy-materials/traceabilitySelect the control boundary before the service catalog/environmentsLocal compute with controlled synchronization/environments/disconnected-edgeRegional enterprise foundation/environments/global-computeDedicated infrastructure and local authority/environments/private-national-cloudIsolated capacity for sensitive workloads/environments/secure-enclaveJurisdiction-aware operations and control/environments/sovereign-regionDirect answers about Talvium's current state/faqBuild regions through bounded roles and measurable evidence/partnersBring one bounded capability or region pathway/partners/becomeDeliver the physical service boundary/partners/energy-infrastructureA qualified directory—not an open catalog/partners/marketplaceBuild local operating authority—not a flag-shaped reseller/partners/national-regionalCompare equivalent scopes before commitment/partners/procurementQualify components inside a declared configuration/partners/technologyA verifiable chain from site rights to workload execution/platformAI that stays inside the approved boundary/platform/aiA portable runtime between infrastructure and mission software/platform/application-platformSecure compute cells that declare their operating envelope/platform/computeGoverned data services with residency visible/platform/dataLocal operation when connectivity is constrained or absent/platform/edgeConnect authorized services without erasing boundaries/platform/federationSecurity claims scoped to the system that earned them/platform/securityThe operational portal is not yet open/portalPrice the verified service boundary—not an imaginary GPU hour/pricingBuild the inputs before asking for a number/pricing/calculatorMatch commitment to mission certainty/pricing/capacity-optionsOptimize cost, capacity, energy, and control together/pricing/finopsChoose the accountable contracting path/pricing/purchase-optionsPrivacy/privacyProduct directory/productsA region is an evidence record, not a dot on a map/regionsA candidate site program governed by evidence gates/regions/africa-site-01Published lifecycle before procurement/regions/availabilityPublish every place data can exist/regions/data-residencyA geography explorer with no decorative availability dots/regions/mapA region enters the roadmap through evidence gates/regions/plannedArchitecture, assurance, and mission preparation/resourcesNo customer outcome is published without approval and evidence/resources/customer-storiesDocumentation organized by decision boundary/resources/documentationBriefings and demonstrations only when the evidence is ready/resources/eventsA dated record of what Talvium has actually changed/resources/newsroomStart with an evidence-producing sequence/resources/quickstartsThree physical patterns, one evidence discipline/resources/reference-architecturesResearch references/resources/referencesDecision briefs for secure compute programs/resources/reportsTreat storage as an engineered service input/solutions/battery-storageCoordinate flexible compute with measured energy conditions/solutions/clean-energyLocal resilience for systems that cannot wait for the network/solutions/critical-infrastructureMove governed decisions—not uncontrolled data/solutions/data-aiA sponsor-specific path from unclassified proof to approved service/solutions/defense-intelligencePublic services with data control built into the deployment/solutions/governmentModernize without losing the control record/solutions/migration-modernizationOperate the mission without turning geology into a marketing claim/solutions/mining-mineralsMake the operating boundary inspectable/solutions/regulated-industriesAccelerated compute with collaboration boundaries intact/solutions/research-industryAccelerated research without surrendering collaboration boundaries/solutions/research-scienceCurrent Talvium lifecycle and availability/statusSupport matched to the service lifecycle/supportTerms/termsEvidence before assurance language/trustGovernment and international assurance catalog/trust/assuranceProtect approved workloads while data is in use/trust/confidential-computingBind data use to purpose, place, people, and time/trust/data-privacyDeclare custody instead of saying ‘encrypted’/trust/encryption-key-controlGovern the model, system, decision, and outcome/trust/responsible-aiName who must make each control true/trust/shared-responsibilitySovereignty is a control model, not a location slogan/trust/sovereigntyPublish readiness, change, and failure at the right scope/trust/transparency